HissenIT
IT Security Awareness News Roundup for October 2026
Added at 10/01/2026, last update at 10/23/2026
What matters most this month in IT security and awareness, and what should guide the attention of CIOs, CISOs, and CEOs? (regularly updated)
General IT Security Awareness Content
Foundation of Cybersecurity Awareness
Build a lasting foundation of cybersecurity awareness that enables your employees to recognize threats, stay vigilant, and make confident decisions in any situation:
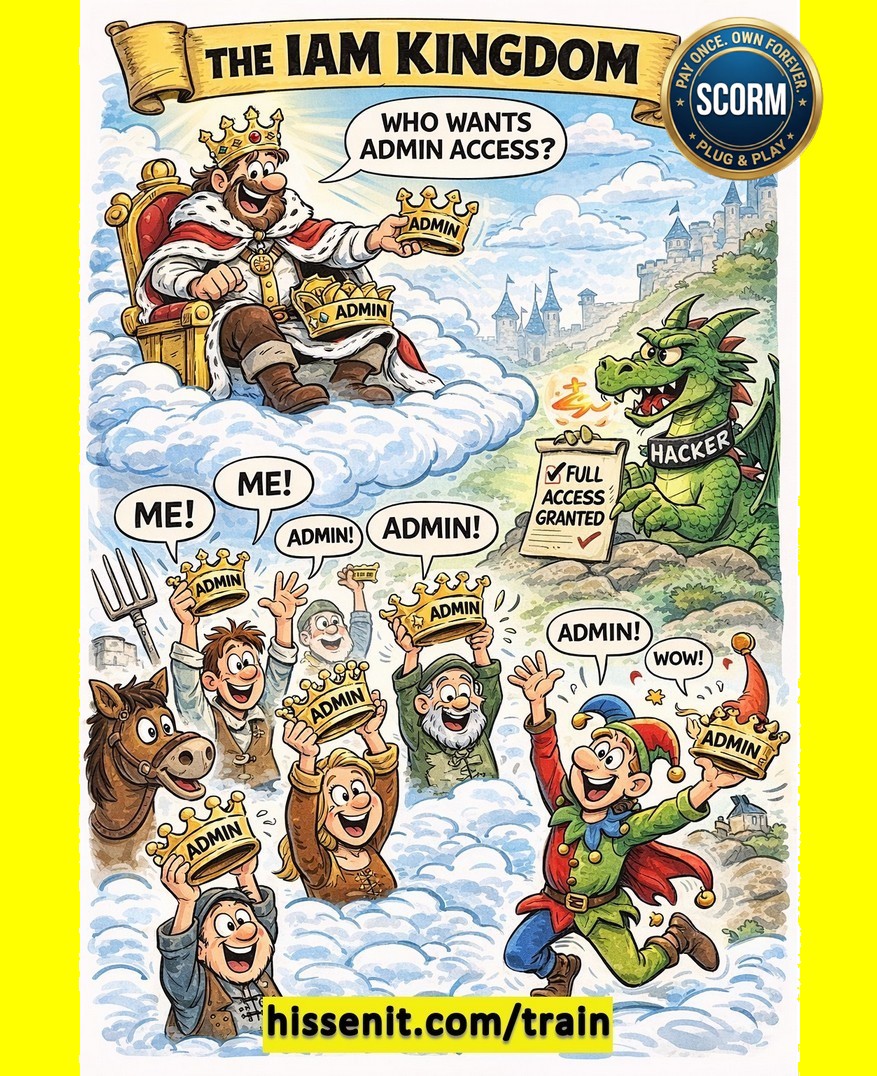
Security Awareness of Managers: Privileged roles in your organization
How do you deal with privileged roles in your organization? Is your documentation always “audit-ready”?
IT Security Awareness Failures
UAT-11985 Uses Fake Event Invitations for AI-Assisted Google Account Phishing
The threat actor tracked as UAT-11985 is targeting individuals affiliated with Taiwanese research organizations using convincing fake event invitations and potentially AI-generated phishing content. The campaign impersonates legitimate academic institutions and uses malicious QR codes and fake Google Forms pages to redirect victims to adversary-in-the-middle (AiTM) phishing infrastructure. The attackers relay Google login requests in real time to steal passwords and multi-factor authentication codes, potentially enabling full account takeover and session compromise. (10/17/2026)
Phishing success: Arizona Courts Cyberattack Exposes Sensitive Data of 1.3 Million
A cyberattack on Arizona's court system exposed personal information linked to approximately 1.3 million people, nearly 30,000 protection orders, and 150,000 foster-care reports. Investigators believe the attack began after a court employee clicked a malicious link in a phishing email, while IT staff detected and stopped the incident. Officials report no evidence that the stolen data has been misused or shared, and court proceedings have not been disrupted. (10/11/2026)
Phishing Toolkit Uses Social Media Ads to Steal Credentials and Payment Data
The Milk Dragon (Nailong) phishing kit uses fake discounts promoted through Facebook and TikTok marketplaces to redirect victims to convincing counterfeit online stores. Using Adversary-in-the-Middle (AiTM) techniques, attackers can capture passwords, MFA codes and session cookies in real time, while the fake checkout pages also harvest payment-card details and one-time verification codes. (10/05/2026)
Secure Programming / Coding Failures
Path Traversal: Cisco Secure E-Mail Gateway Vulnerability Exploited in Active Attacks
Cisco has warned of active attacks exploiting a critical vulnerability (CVE-2026-76519, CVSS 9.8) in its Secure E-Mail Gateway appliances, potentially allowing unauthenticated attackers to write files to the underlying operating system and execute commands as root. Exploitation involves sending an e-mail with a specially crafted attachment to a vulnerable gateway with specific security features enabled. Administrators should verify that Content Scanner Tools version 25.3.0.5525 or later is installed, apply the relevant security updates, and check for indicators of compromise. (10/17/2026)